Jellyfin SSO plugin used to work seamlessly with the LDAP Authentication plugin.
With this fork, enabling the LDAP Auth plugin causes an error on OIDC init. Withot LDAP Auth users are forced to use Quick Connect to login to apps.
[2026-10-27 17:04:19.155 +08:00] [INF] OIDC Controller initialized
[2026-10-27 17:04:19.155 +08:00] [ERR] Error processing request. URL "GET" "/oidc/start/Authelia".
System.NullReferenceException: Object reference not set to an instance of an object.
at Jellyfin.Plugin.OIDC_Auth.Api.OIDCController.Invalidate()
at Jellyfin.Plugin.OIDC_Auth.Api.OIDCController.OIDCChallenge(String provider, Boolean isLinking)
at lambda_method24325(Closure, Object)
at Microsoft.AspNetCore.Mvc.Infrastructure.ActionMethodExecutor.TaskOfActionResultExecutor.Execute(ActionContext actionContext, IActionResultTypeMapper mapper, ObjectMethodExecutor executor, Object controller, Object[] arguments)
at Microsoft.AspNetCore.Mvc.Infrastructure.ControllerActionInvoker.<InvokeActionMethodAsync>g__Awaited|12_0(ControllerActionInvoker invoker, ValueTask`1 actionResultValueTask)
at Microsoft.AspNetCore.Mvc.Infrastructure.ControllerActionInvoker.<InvokeNextActionFilterAsync>g__Awaited|10_0(ControllerActionInvoker invoker, Task lastTask, State next, Scope scope, Object state, Boolean isCompleted)
at Microsoft.AspNetCore.Mvc.Infrastructure.ControllerActionInvoker.Rethrow(ActionExecutedContextSealed context)
at Microsoft.AspNetCore.Mvc.Infrastructure.ControllerActionInvoker.InvokeInnerFilterAsync()
--- End of stack trace from previous location ---
at Microsoft.AspNetCore.Mvc.Infrastructure.ResourceInvoker.<InvokeNextResourceFilter>g__Awaited|25_0(ResourceInvoker invoker, Task lastTask, State next, Scope scope, Object state, Boolean isCompleted)
at Microsoft.AspNetCore.Mvc.Infrastructure.ResourceInvoker.Rethrow(ResourceExecutedContextSealed context)
at Microsoft.AspNetCore.Mvc.Infrastructure.ResourceInvoker.Next(State& next, Scope& scope, Object& state, Boolean& isCompleted)
at Microsoft.AspNetCore.Mvc.Infrastructure.ResourceInvoker.InvokeFilterPipelineAsync()
--- End of stack trace from previous location ---
at Microsoft.AspNetCore.Mvc.Infrastructure.ResourceInvoker.<InvokeAsync>g__Awaited|17_0(ResourceInvoker invoker, Task task, IDisposable scope)
at Jellyfin.Api.Middleware.ServerStartupMessageMiddleware.Invoke(HttpContext httpContext, IServerApplicationHost serverApplicationHost, ILocalizationManager localizationManager)
at Jellyfin.Api.Middleware.WebSocketHandlerMiddleware.Invoke(HttpContext httpContext, IWebSocketManager webSocketManager)
at Jellyfin.Api.Middleware.IPBasedAccessValidationMiddleware.Invoke(HttpContext httpContext, INetworkManager networkManager)
at Microsoft.AspNetCore.Authorization.AuthorizationMiddleware.Invoke(HttpContext context)
at Jellyfin.Api.Middleware.QueryStringDecodingMiddleware.Invoke(HttpContext httpContext)
at Swashbuckle.AspNetCore.ReDoc.ReDocMiddleware.Invoke(HttpContext httpContext)
at Swashbuckle.AspNetCore.SwaggerUI.SwaggerUIMiddleware.Invoke(HttpContext httpContext)
at Swashbuckle.AspNetCore.Swagger.SwaggerMiddleware.Invoke(HttpContext httpContext, ISwaggerProvider swaggerProvider)
at Microsoft.AspNetCore.Authentication.AuthenticationMiddleware.Invoke(HttpContext context)
at Jellyfin.Api.Middleware.RobotsRedirectionMiddleware.Invoke(HttpContext httpContext)
at Microsoft.AspNetCore.Localization.RequestLocalizationMiddleware.Invoke(HttpContext context)
at Microsoft.AspNetCore.ResponseCompression.ResponseCompressionMiddleware.InvokeCore(HttpContext context)
at Jellyfin.Api.Middleware.ResponseTimeMiddleware.Invoke(HttpContext context, IServerConfigurationManager serverConfigurationManager)
at Jellyfin.Api.Middleware.ExceptionMiddleware.Invoke(HttpContext context)
Jellyfin SSO plugin used to work seamlessly with the LDAP Authentication plugin.
With this fork, enabling the LDAP Auth plugin causes an error on OIDC init. Withot LDAP Auth users are forced to use Quick Connect to login to apps.
```
[2026-10-27 17:04:19.155 +08:00] [INF] OIDC Controller initialized
[2026-10-27 17:04:19.155 +08:00] [ERR] Error processing request. URL "GET" "/oidc/start/Authelia".
System.NullReferenceException: Object reference not set to an instance of an object.
at Jellyfin.Plugin.OIDC_Auth.Api.OIDCController.Invalidate()
at Jellyfin.Plugin.OIDC_Auth.Api.OIDCController.OIDCChallenge(String provider, Boolean isLinking)
at lambda_method24325(Closure, Object)
at Microsoft.AspNetCore.Mvc.Infrastructure.ActionMethodExecutor.TaskOfActionResultExecutor.Execute(ActionContext actionContext, IActionResultTypeMapper mapper, ObjectMethodExecutor executor, Object controller, Object[] arguments)
at Microsoft.AspNetCore.Mvc.Infrastructure.ControllerActionInvoker.<InvokeActionMethodAsync>g__Awaited|12_0(ControllerActionInvoker invoker, ValueTask`1 actionResultValueTask)
at Microsoft.AspNetCore.Mvc.Infrastructure.ControllerActionInvoker.<InvokeNextActionFilterAsync>g__Awaited|10_0(ControllerActionInvoker invoker, Task lastTask, State next, Scope scope, Object state, Boolean isCompleted)
at Microsoft.AspNetCore.Mvc.Infrastructure.ControllerActionInvoker.Rethrow(ActionExecutedContextSealed context)
at Microsoft.AspNetCore.Mvc.Infrastructure.ControllerActionInvoker.InvokeInnerFilterAsync()
--- End of stack trace from previous location ---
at Microsoft.AspNetCore.Mvc.Infrastructure.ResourceInvoker.<InvokeNextResourceFilter>g__Awaited|25_0(ResourceInvoker invoker, Task lastTask, State next, Scope scope, Object state, Boolean isCompleted)
at Microsoft.AspNetCore.Mvc.Infrastructure.ResourceInvoker.Rethrow(ResourceExecutedContextSealed context)
at Microsoft.AspNetCore.Mvc.Infrastructure.ResourceInvoker.Next(State& next, Scope& scope, Object& state, Boolean& isCompleted)
at Microsoft.AspNetCore.Mvc.Infrastructure.ResourceInvoker.InvokeFilterPipelineAsync()
--- End of stack trace from previous location ---
at Microsoft.AspNetCore.Mvc.Infrastructure.ResourceInvoker.<InvokeAsync>g__Awaited|17_0(ResourceInvoker invoker, Task task, IDisposable scope)
at Jellyfin.Api.Middleware.ServerStartupMessageMiddleware.Invoke(HttpContext httpContext, IServerApplicationHost serverApplicationHost, ILocalizationManager localizationManager)
at Jellyfin.Api.Middleware.WebSocketHandlerMiddleware.Invoke(HttpContext httpContext, IWebSocketManager webSocketManager)
at Jellyfin.Api.Middleware.IPBasedAccessValidationMiddleware.Invoke(HttpContext httpContext, INetworkManager networkManager)
at Microsoft.AspNetCore.Authorization.AuthorizationMiddleware.Invoke(HttpContext context)
at Jellyfin.Api.Middleware.QueryStringDecodingMiddleware.Invoke(HttpContext httpContext)
at Swashbuckle.AspNetCore.ReDoc.ReDocMiddleware.Invoke(HttpContext httpContext)
at Swashbuckle.AspNetCore.SwaggerUI.SwaggerUIMiddleware.Invoke(HttpContext httpContext)
at Swashbuckle.AspNetCore.Swagger.SwaggerMiddleware.Invoke(HttpContext httpContext, ISwaggerProvider swaggerProvider)
at Microsoft.AspNetCore.Authentication.AuthenticationMiddleware.Invoke(HttpContext context)
at Jellyfin.Api.Middleware.RobotsRedirectionMiddleware.Invoke(HttpContext httpContext)
at Microsoft.AspNetCore.Localization.RequestLocalizationMiddleware.Invoke(HttpContext context)
at Microsoft.AspNetCore.ResponseCompression.ResponseCompressionMiddleware.InvokeCore(HttpContext context)
at Jellyfin.Api.Middleware.ResponseTimeMiddleware.Invoke(HttpContext context, IServerConfigurationManager serverConfigurationManager)
at Jellyfin.Api.Middleware.ExceptionMiddleware.Invoke(HttpContext context)
```
@sgerq2f I'm not sure what caused this error C# appears to be inlining function calls as the stack trace doesn't appear to be complete. but this appears to be an issue where a request went through before the plugin was fully loaded
I've released 6.0.0.6 and it should fix it.
If you have the time and patience try it again and see if it works.
@sgerq2f I'm not sure what caused this error C# appears to be inlining function calls as the stack trace doesn't appear to be complete. but this appears to be an issue where a request went through before the plugin was fully loaded
I've released 6.0.0.6 and it should fix it.
If you have the time and patience try it again and see if it works.
Only other remaining issue is that this plugin forces the user's Authentication provider from LDAP to Default.
Are there any potential workarounds for this?
Thanks, the error seems to be resolved.
Only other remaining issue is that this plugin forces the user's Authentication provider from LDAP to Default.
Are there any potential workarounds for this?
If you want the same provider for every OIDC user you can go to the OIDC settings and set it here
It should only change it if the Authentication provider is blank.
Can you check the log for any lines with `Set default login provider`
If you have different providers for different users can set the `AuthenticationProviderId` in a custom claim from your OIDC server. See https://gitea.narnian.us/lordwelch/jellyfin-plugin-oidc#setting-custom-claims
If you want the same provider for every OIDC user you can go to the OIDC settings and set it here 
Blocking a user prevents them from interacting with repositories, such as opening or commenting on pull requests or issues. Learn more about blocking a user.
Jellyfin SSO plugin used to work seamlessly with the LDAP Authentication plugin.
With this fork, enabling the LDAP Auth plugin causes an error on OIDC init. Withot LDAP Auth users are forced to use Quick Connect to login to apps.
@sgerq2f I'm not sure what caused this error C# appears to be inlining function calls as the stack trace doesn't appear to be complete. but this appears to be an issue where a request went through before the plugin was fully loaded
I've released 6.0.0.6 and it should fix it.
If you have the time and patience try it again and see if it works.
Thanks, the error seems to be resolved.
Only other remaining issue is that this plugin forces the user's Authentication provider from LDAP to Default.
Are there any potential workarounds for this?
It should only change it if the Authentication provider is blank.
Can you check the log for any lines with
Set default login providerIf you have different providers for different users can set the
AuthenticationProviderIdin a custom claim from your OIDC server. See https://gitea.narnian.us/lordwelch/jellyfin-plugin-oidc#setting-custom-claimsIf you want the same provider for every OIDC user you can go to the OIDC settings and set it here
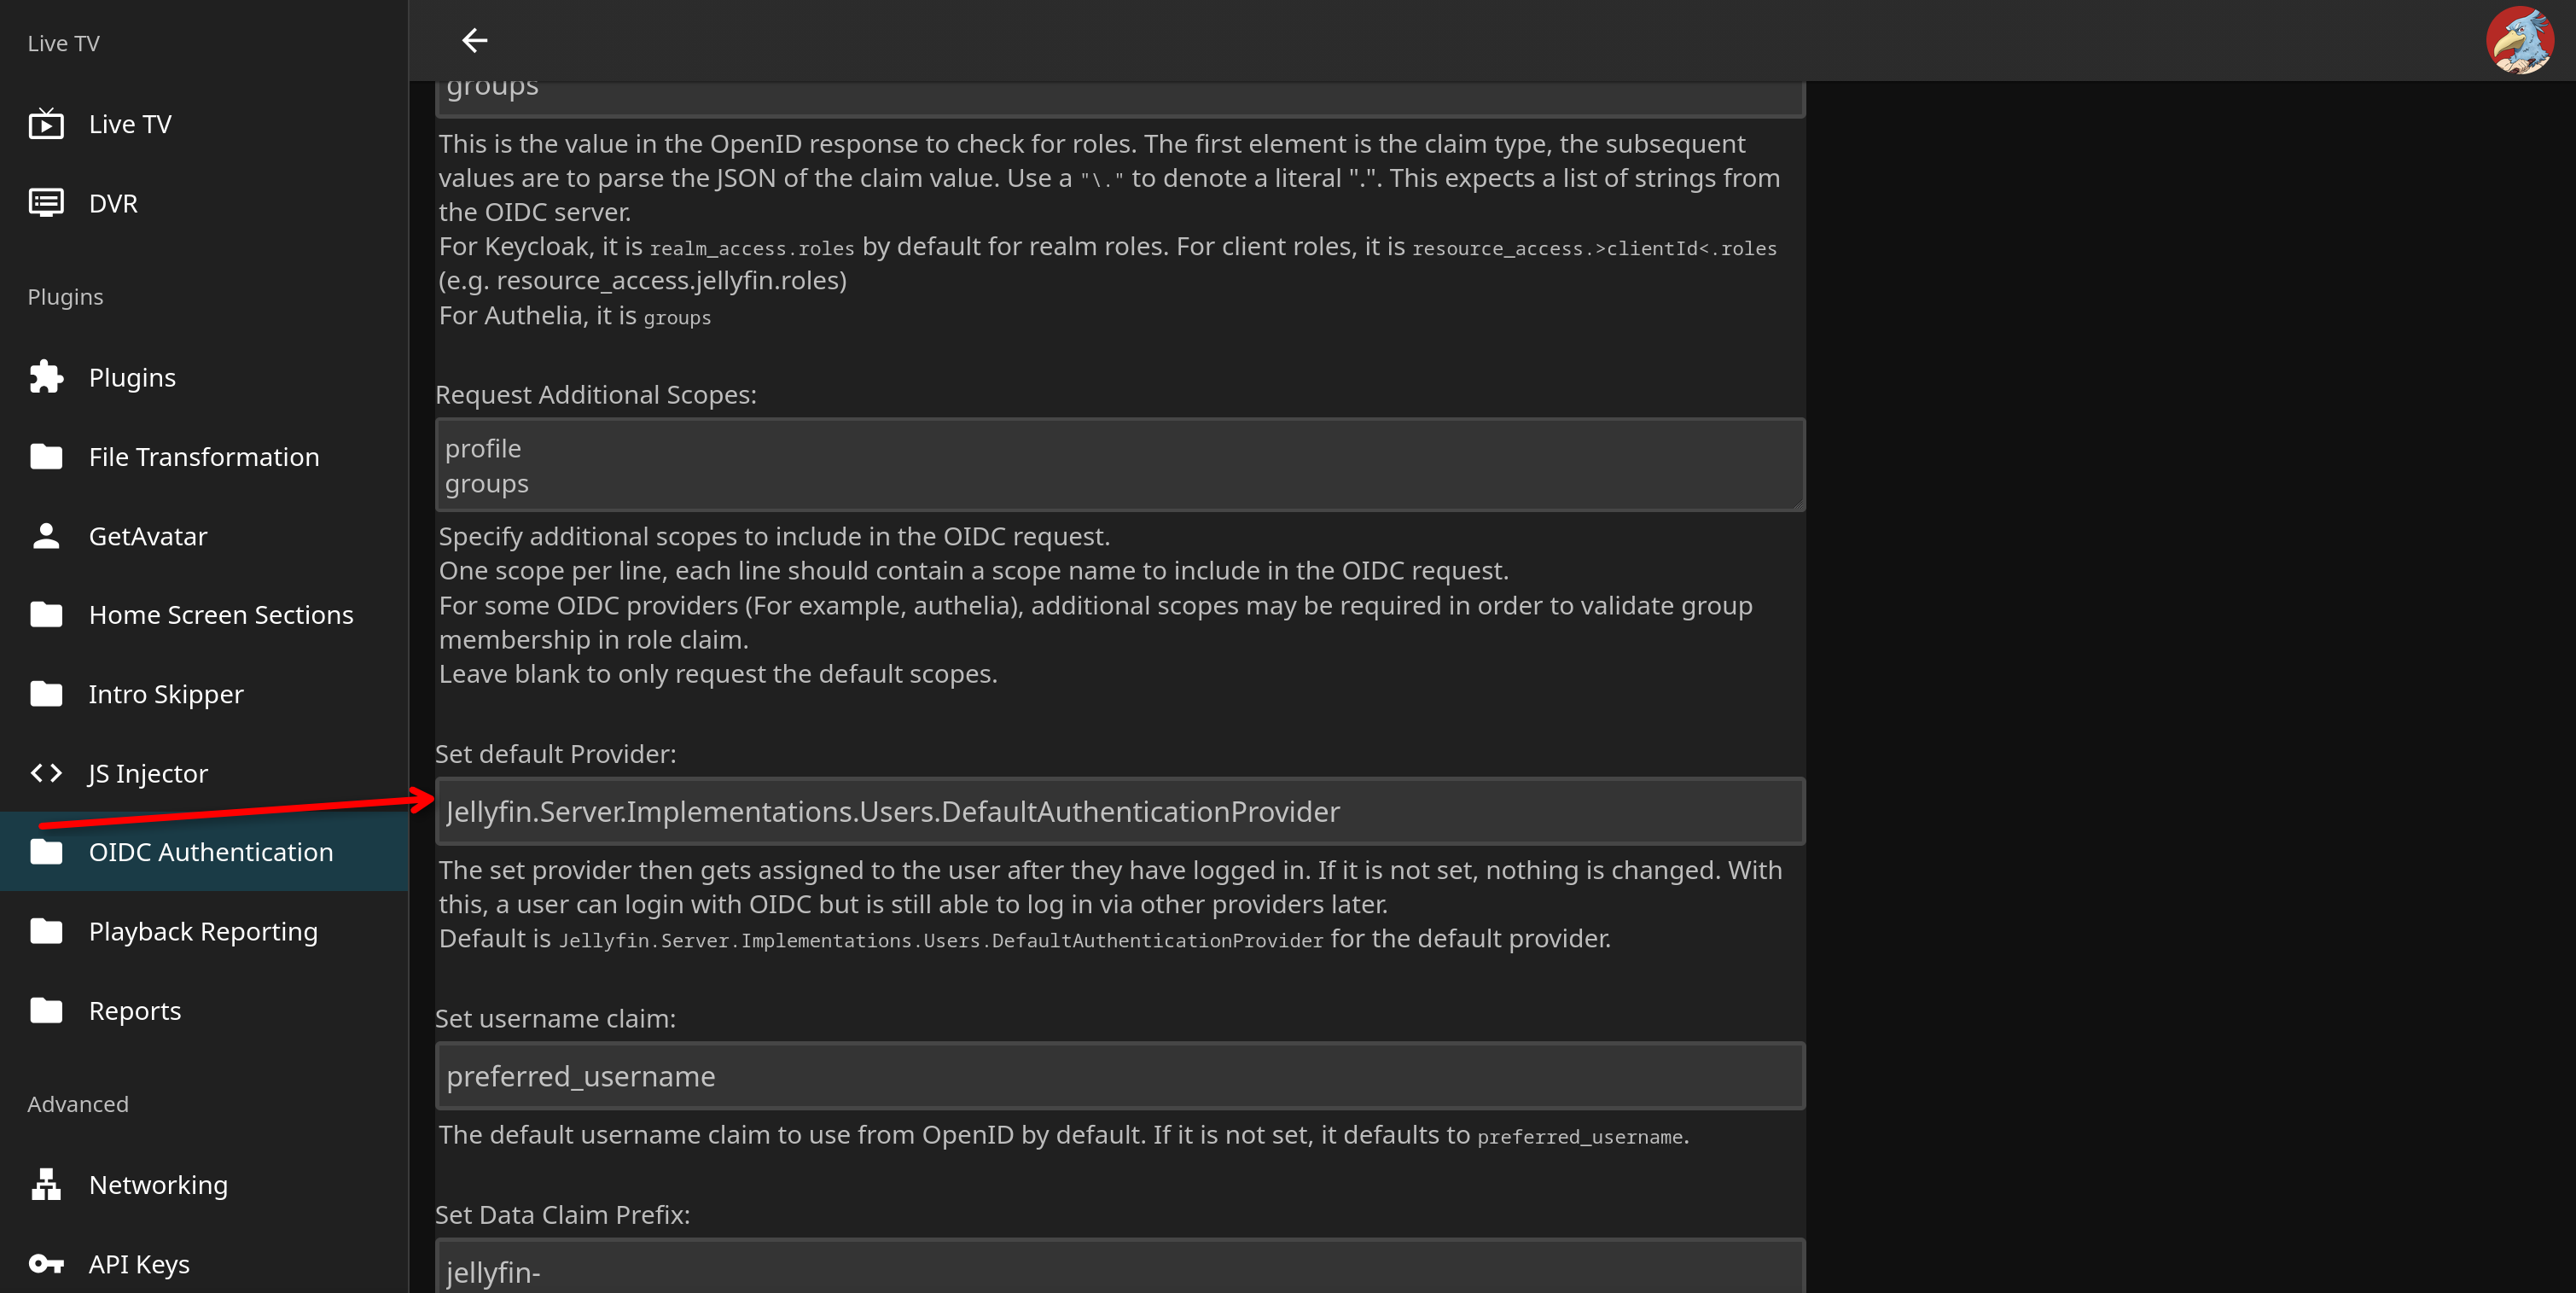
You can also just remove the value from the
Set default Provideroption. That will make sure it doesn't set a defaultAh wonderful, I missed that setting. Thanks!